1. Why should businesses prioritize data protection?
Business data includes many different types of information, such as customer data, financial records, internal documents, and operational information considered trade secrets. Each type of data has its own value and becomes an attractive target for cyberattackers, especially as businesses undergo digital transformation and store an increasing amount of information online.
When a data breach occurs, meaning data is leaked or lost, businesses face serious consequences. Brand reputation suffers, customers lose trust, and in many cases businesses also bear legal liability if data is mishandled. The cost of remediation, from investigating the root cause to restoring systems, is often far greater than the cost of preventive investment.
Current cyberattack trends focus heavily on the web application layer, where businesses typically store and process data directly. Common attack methods include exploiting application vulnerabilities, denial of service attacks that disrupt data access, and phishing tactics targeting internal employees. As a result, deploying multiple layers of data protection at once, from legal compliance to internal governance and web application security, has become a mandatory requirement rather than an option.
2. Legal regulations on data protection in Vietnam
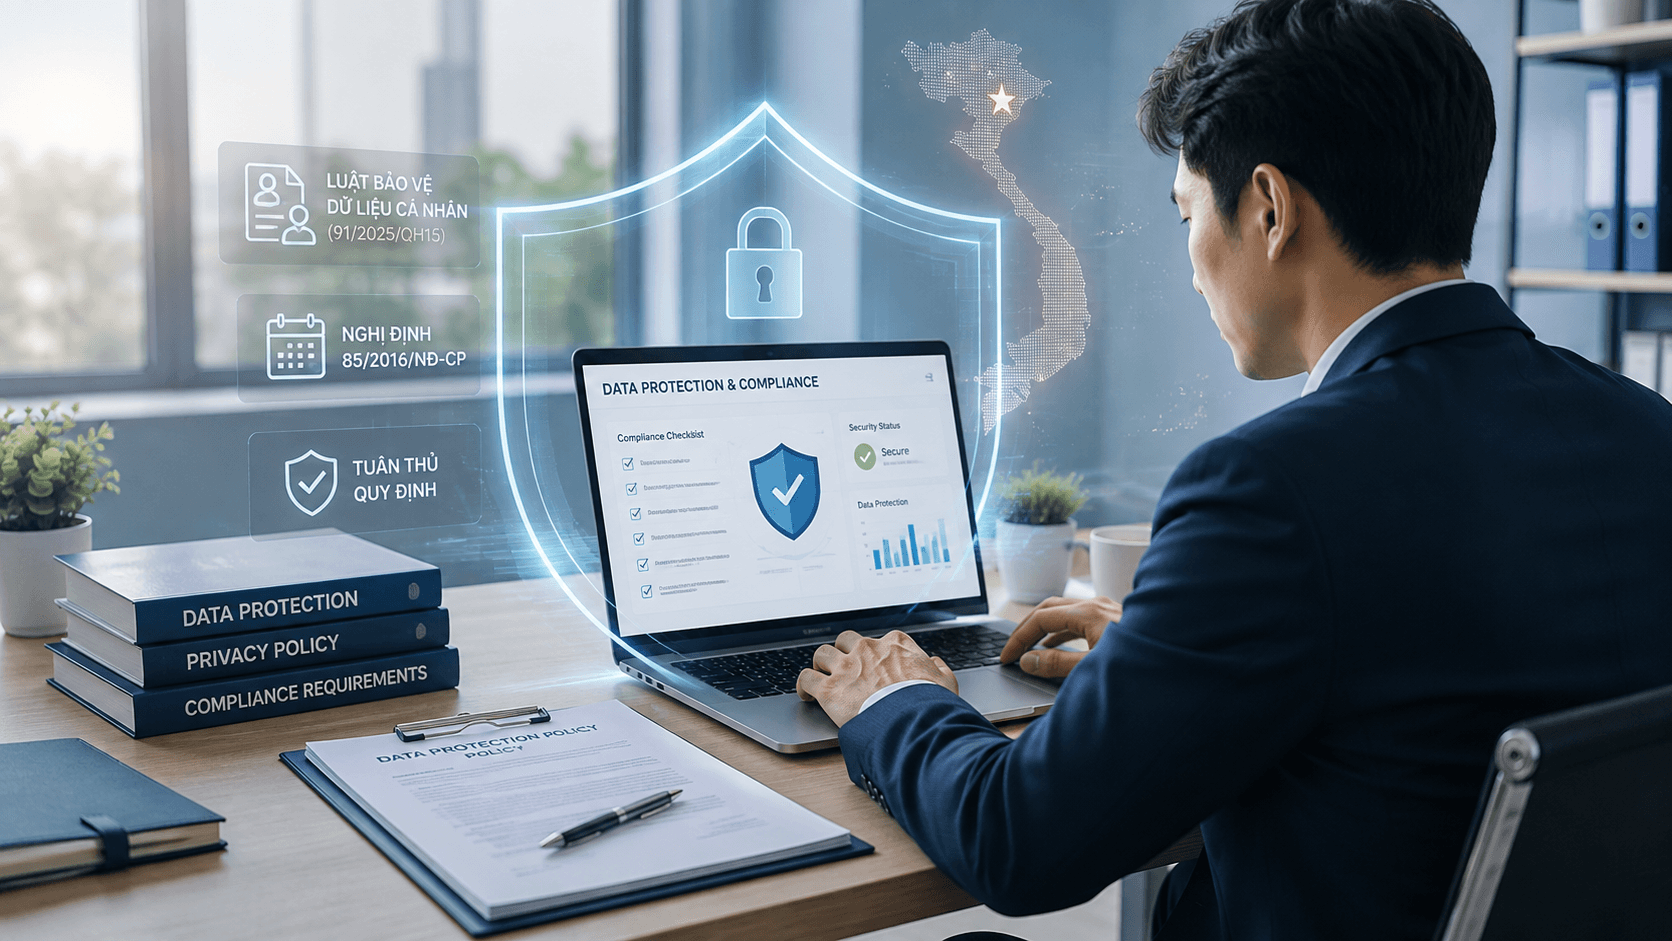
Data protection is not only a technology requirement but also a legal obligation. Vietnam’s legal framework on cybersecurity and data has just undergone a major update between 2025 and 2026, and businesses need to understand these changes clearly to avoid relying on documents that are no longer in effect.
2.1. Cybersecurity Law 2025 (No. 116/2025/QH15)
On December 10, 2025, the 15th National Assembly passed the Cybersecurity Law 2025, numbered 116/2025/QH15, comprising 8 chapters and 58 articles, 15 more articles than the 2018 Cybersecurity Law. This law officially takes effect on July 1, 2026, and simultaneously replaces two earlier documents: the 2018 Cybersecurity Law (No. 24/2018/QH14) and the 2015 Law on Network Information Security (No. 86/2015/QH13). Merging the two former laws addresses the previous overlap in regulatory authority between the Ministry of Public Security and the Ministry of Information and Communications, while also unifying the concept of "cybersecurity" in place of "network information security."
Businesses providing services in cyberspace in Vietnam should note the responsibilities carried over and expanded under the new law, including warning users of cybersecurity risks, developing incident response plans, and applying technical solutions to prevent data leakage or loss during information collection and processing.
2.2. Decree 85/2016/ND-CP and Circular 12/2022/TT-BTTTT
Decree 85/2016/ND-CP classifies information systems in Vietnam into 5 security levels, based on their level of importance and the scope of impact should an incident occur. According to the appendix issued with Circular 12/2022/TT-BTTTT guiding Decree 85/2016/ND-CP, level 2 information systems (under Clause 2, Article 8 of Decree 85/2016/ND-CP), or level 3 and above, are required to use a web application firewall product.
It is worth noting that both of these documents were issued under the 2015 Law on Network Information Security, which ceased to be effective on July 1, 2026, when the 2025 Cybersecurity Law officially took effect. At the time this article was updated, regulators had not yet issued an official replacement decree for classifying information system security levels under the new legal framework, so Decree 85/2016/ND-CP and Circular 12/2022/TT-BTTTT remain in effect during this transition period. Businesses with information systems at level 2 (under Clause 2, Article 8 of Decree 85/2016/ND-CP) or level 3 and above should proactively review their current compliance status and monitor for new guiding documents once issued.
2.3. Personal Data Protection Law (No. 91/2025/QH15)
The Personal Data Protection Law No. 91/2025/QH15 was passed by the National Assembly on June 26, 2025, and officially took effect on January 1, 2026. This is Vietnam’s first dedicated law comprehensively governing the collection, processing, and protection of personal data, replacing the earlier Decree 13/2023/ND-CP. Decree 356/2025/ND-CP, issued on December 31, 2025, and effective the same day as the law, sets out detailed procedures and implementation measures.
Businesses that collect customer data such as contact information, purchasing behavior, or biometric data all fall within the scope of this law, regardless of organizational size. Compliance not only helps businesses avoid legal risk but also strengthens customer trust during transactions.
| Legal document | Effective date | Key content |
| Cybersecurity Law 2025 (No. 116/2025/QH15) | July 1, 2026 | Replaces the 2018 Cybersecurity Law and the 2015 Law on Network Information Security |
| Decree 85/2016/ND-CP and Circular 12/2022/TT-BTTTT | Decree: July 1, 2016. Circular: October 1, 2022 | Classifies information systems into 5 security levels; mandates a WAF for level 2 systems (under Clause 2, Article 8 of Decree 85/2016/ND-CP) or level 3 and above |
| Personal Data Protection Law (No. 91/2025/QH15) and Decree 356/2025/ND-CP | January 1, 2026 | Governs the collection, processing, and protection of personal data |
| Decree 332/2026/ND-CP | August 19, 2026 | Trading of cybersecurity products and services |
3. Data protection measures businesses should implement
To meet the legal requirements above and reduce the risk of data leaks, businesses need to deploy multiple layers of protection together, from internal governance to web application security. These are data protection measures that any organization, large or small, should adopt.
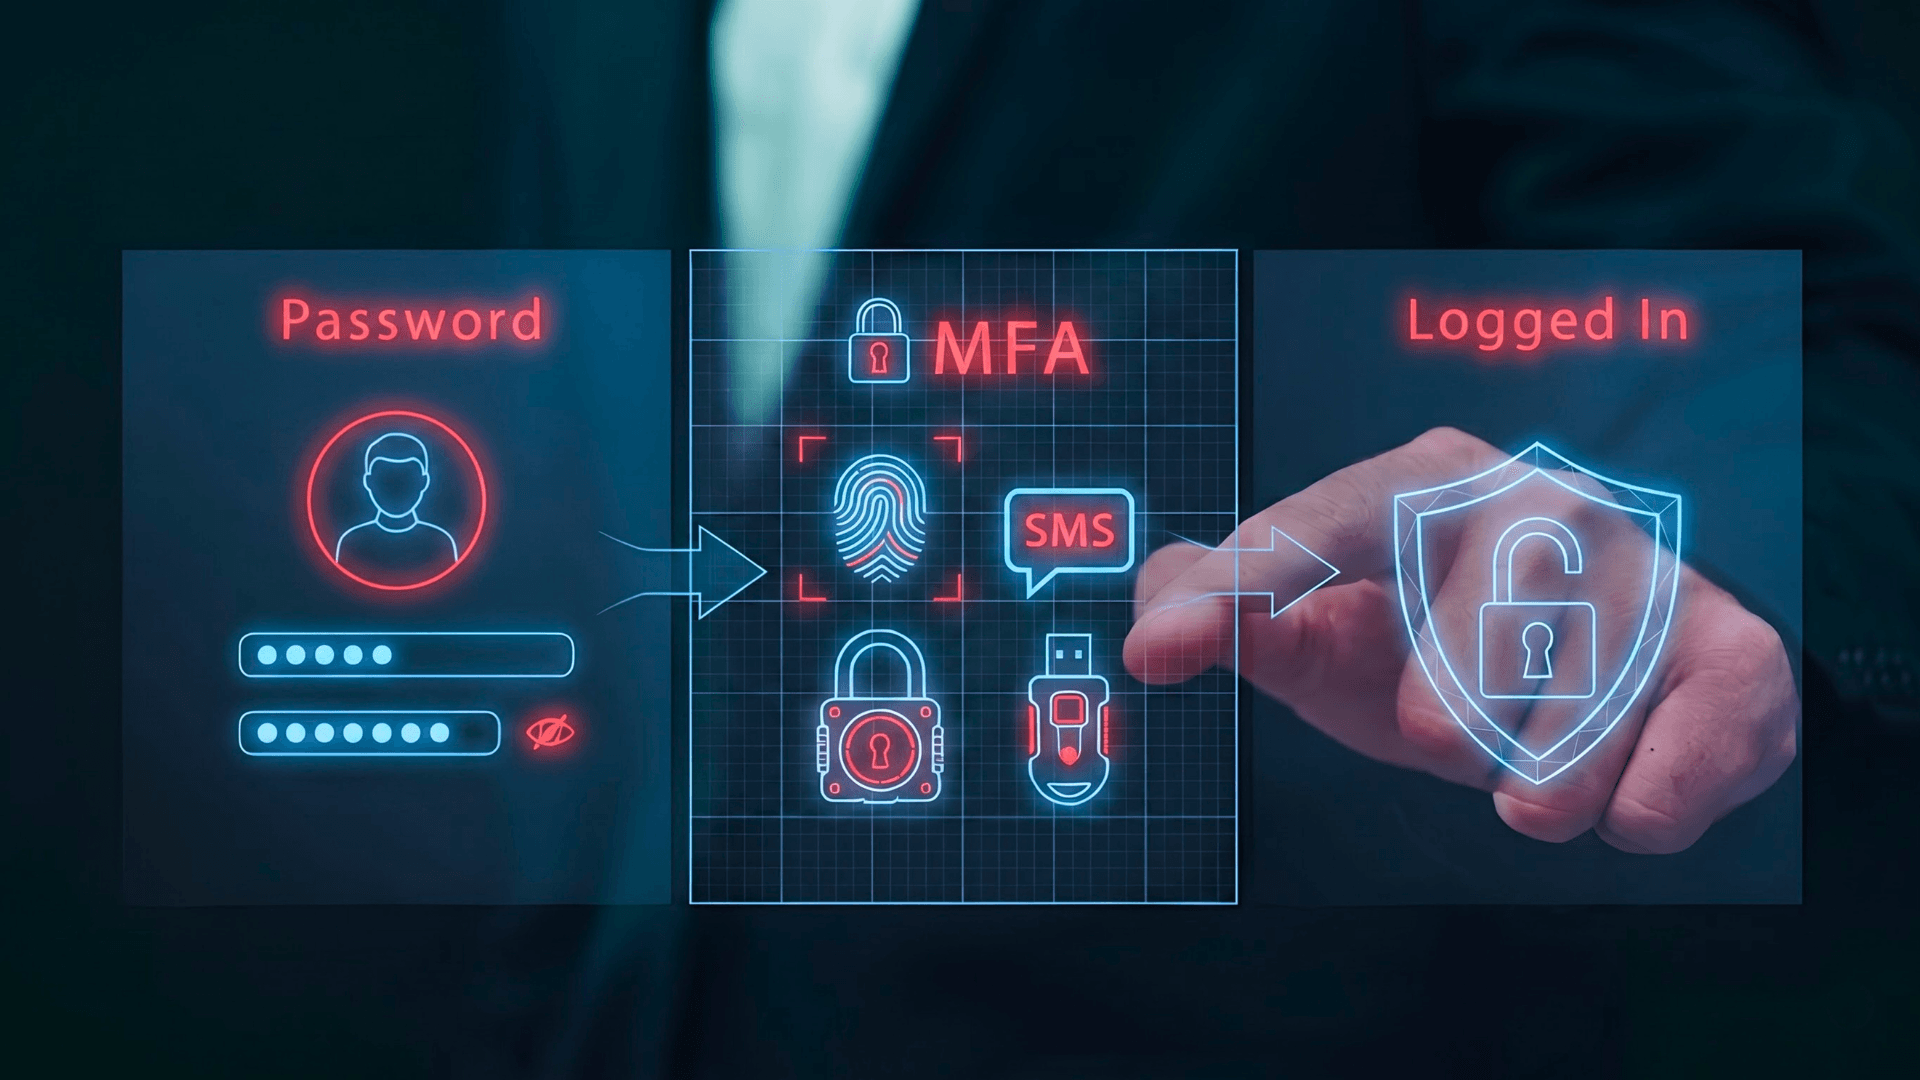
3.1. Access control and multi-factor authentication
Access control is a measure that helps businesses tightly manage who is allowed to access which type of data, through identity verification and corresponding permission assignment for each user. Access is typically assigned based on job role, department, or seniority, ensuring each employee can only access the scope of data necessary for their work.
In addition to access control, multi-factor authentication (MFA) adds another layer of protection by requiring users to verify their identity through multiple methods, for example an OTP code sent to their phone combined with a login password. Businesses can apply tools such as SSH keys to protect remote access to servers, or a centralized identity management system with MFA enabled to easily grant and revoke permissions as personnel change, minimizing the risk of data leakage from excessive access or compromised accounts.
3.2. Applying the Zero Trust model to data access control
The Zero Trust model operates on the principle of not automatically trusting any access, even from within the internal network. Every data access request must be authenticated and have its permissions verified before being approved. This approach helps reduce risk when an employee’s account is compromised or when an unfamiliar device attempts to access a system containing important data, and it is typically deployed alongside access control and MFA to form a complete identity control layer starting at the network infrastructure level.
3.3. Encrypting data at rest and in transit
Data encryption is the process of converting information into a form that cannot be read without the appropriate decryption key. This measure needs to be applied in both states of data, at rest on servers or devices and in transit between systems over a network. Even if data is stolen, proper encryption renders the information worthless to an attacker who does not possess the decryption key.
3.4. Regular data backup using the 3-2-1 strategy
Regular data backup helps businesses recover information quickly when incidents occur, such as hardware failure, accidental operations, or ransomware attacks. The 3-2-1 strategy is widely adopted by businesses, involving keeping 3 copies of data, on 2 different types of storage media, with 1 copy stored in a location separate from the main system. Businesses can combine cloud storage with local backups to improve recovery capability when an incident occurs.
3.5. Monitoring and logging abnormal access
Continuously monitoring data access activity helps businesses detect abnormal behavior early, before it causes significant damage. Fully logging login information, access times, and actions performed on the system also makes it easier to trace the source when an incident occurs. Without a monitoring mechanism in place, businesses typically only discover a data leak after the damage has already spread, making remediation far more difficult and costly.
3.6. Security awareness training for employees
Many data leak incidents originate from human error, such as employees clicking on phishing links or using weak passwords. Businesses need to organize regular security awareness training to help employees recognize phishing emails, understand proper procedures for handling customer data, and know how to report incidents promptly. This is a low cost measure with a clearly effective reduction in risk, and it is especially suitable for businesses that do not yet have a dedicated security team. It is also an important transitional step before moving on to the defense layer at the software application level, since employees are the ones who directly operate those applications every day.
3.7. Securing the web application layer
At the software layer, where businesses directly process data through websites and applications, the two most common risk groups that need to be controlled are data exploitation vulnerabilities and service disruption attacks. SQL injection and XSS are two of the most common vulnerabilities on the OWASP Top 10 list, frequently exploited by attackers to steal data directly from a database or a user’s browser. With SQL injection, attackers insert malicious code into input fields to make unauthorized queries against a database, while XSS exploits vulnerabilities in a web interface to steal login session information or users’ personal data. OWASP, a non-profit organization dedicated to researching web application security, regularly updates this list of vulnerabilities to help businesses prioritize the right fixes.
To better visualize how dangerous an XSS vulnerability can be, you can watch a demo video simulating a real XSS attack and how WAF Free detects and blocks the malicious payload before it reaches user data:
Alongside the risk of data theft through application vulnerabilities, DDoS attacks, while not directly stealing data, can bring a system down, preventing businesses from accessing or processing data in time during important situations such as financial transactions or customer service. Deploying protection against SQL injection and XSS together with multi-layer DDoS mitigation helps protect data comprehensively at the web application layer, both blocking data theft and maintaining system availability even while under high-volume attack.
3.8. Summary table of business data protection measures
| Measure | Main purpose | Risk if ignored |
| Access control and MFA | Limit access scope by role; multi-layer authentication | Employees or attackers access data beyond their authorized scope |
| Zero Trust | Access control without default trust | A compromised account can easily spread its access |
| Data encryption | Protect data if stolen | Data can be read directly if leaked |
| Regular backup | Recover data when an incident occurs | Permanent data loss when a system fails |
| Access monitoring | Early detection of abnormal behavior | Data leaks discovered too late |
| Employee training | Reduce risk from human error | Employees unintentionally create openings for phishing attacks |
| Web application security | Block data theft and maintain system availability | Data stolen or system down, disrupting transactions |
4. The data protection cost challenge for small and medium businesses
The pressure to protect data comes not only from the threat of attacks but also from the cost of investment, particularly for small and medium businesses. According to a survey published by VNETWORK on VietNamNet in 2026, as many as 42.1% of businesses face budget difficulties for security, most of them small businesses. Meanwhile, the number of cyberattacks targeting domestic businesses continues to rise, making the challenge of balancing budget against the level of data protection more urgent than ever.
Notably, even businesses that have already allocated budget for security are not guaranteed a corresponding level of protection. According to the report "Vietnam Enterprise Cybersecurity Landscape 2026" by VNETWORK, cited by Tuoi Tre, only about 33% of Vietnamese businesses have multi-layered security systems, while DDoS attacks affected 57% of businesses surveyed in 2025. This shows that the issue is not only whether a business invests in security, but whether it invests in the right place, at the defense layer the business is actually missing.
In practice, the cost of data protection does not necessarily scale in proportion to the size of the investment. Many security solutions today are designed on a free or low cost model, helping small businesses access data protection technology from the very start without needing a dedicated technical team or complex infrastructure. This is also an approach widely adopted by cybersecurity providers in Vietnam to help the small and medium business community overcome budget barriers.
5. WAF Free - A Free Web/App Protection Solution for Businesses
To help businesses solve the cost challenge described above, while also contributing to data protection at the web application layer, VNETWORK offers a web application firewall, WAF Free, a free starting solution within the Web/App/API security ecosystem, VNIS, suited to SMEs that want to access this technology without a large budget or a dedicated technical team.
Highlights of WAF Free include:
- Easy integration: Simple configuration in just 2 minutes, requiring no in-depth expertise
- Comprehensive protection: Effectively blocks OWASP Top 10 vulnerabilities and defends against DDoS threats, keeping the website running stably
- Faster content delivery: Optimizes Web/App content delivery performance and improves user experience thanks to CDN infrastructure
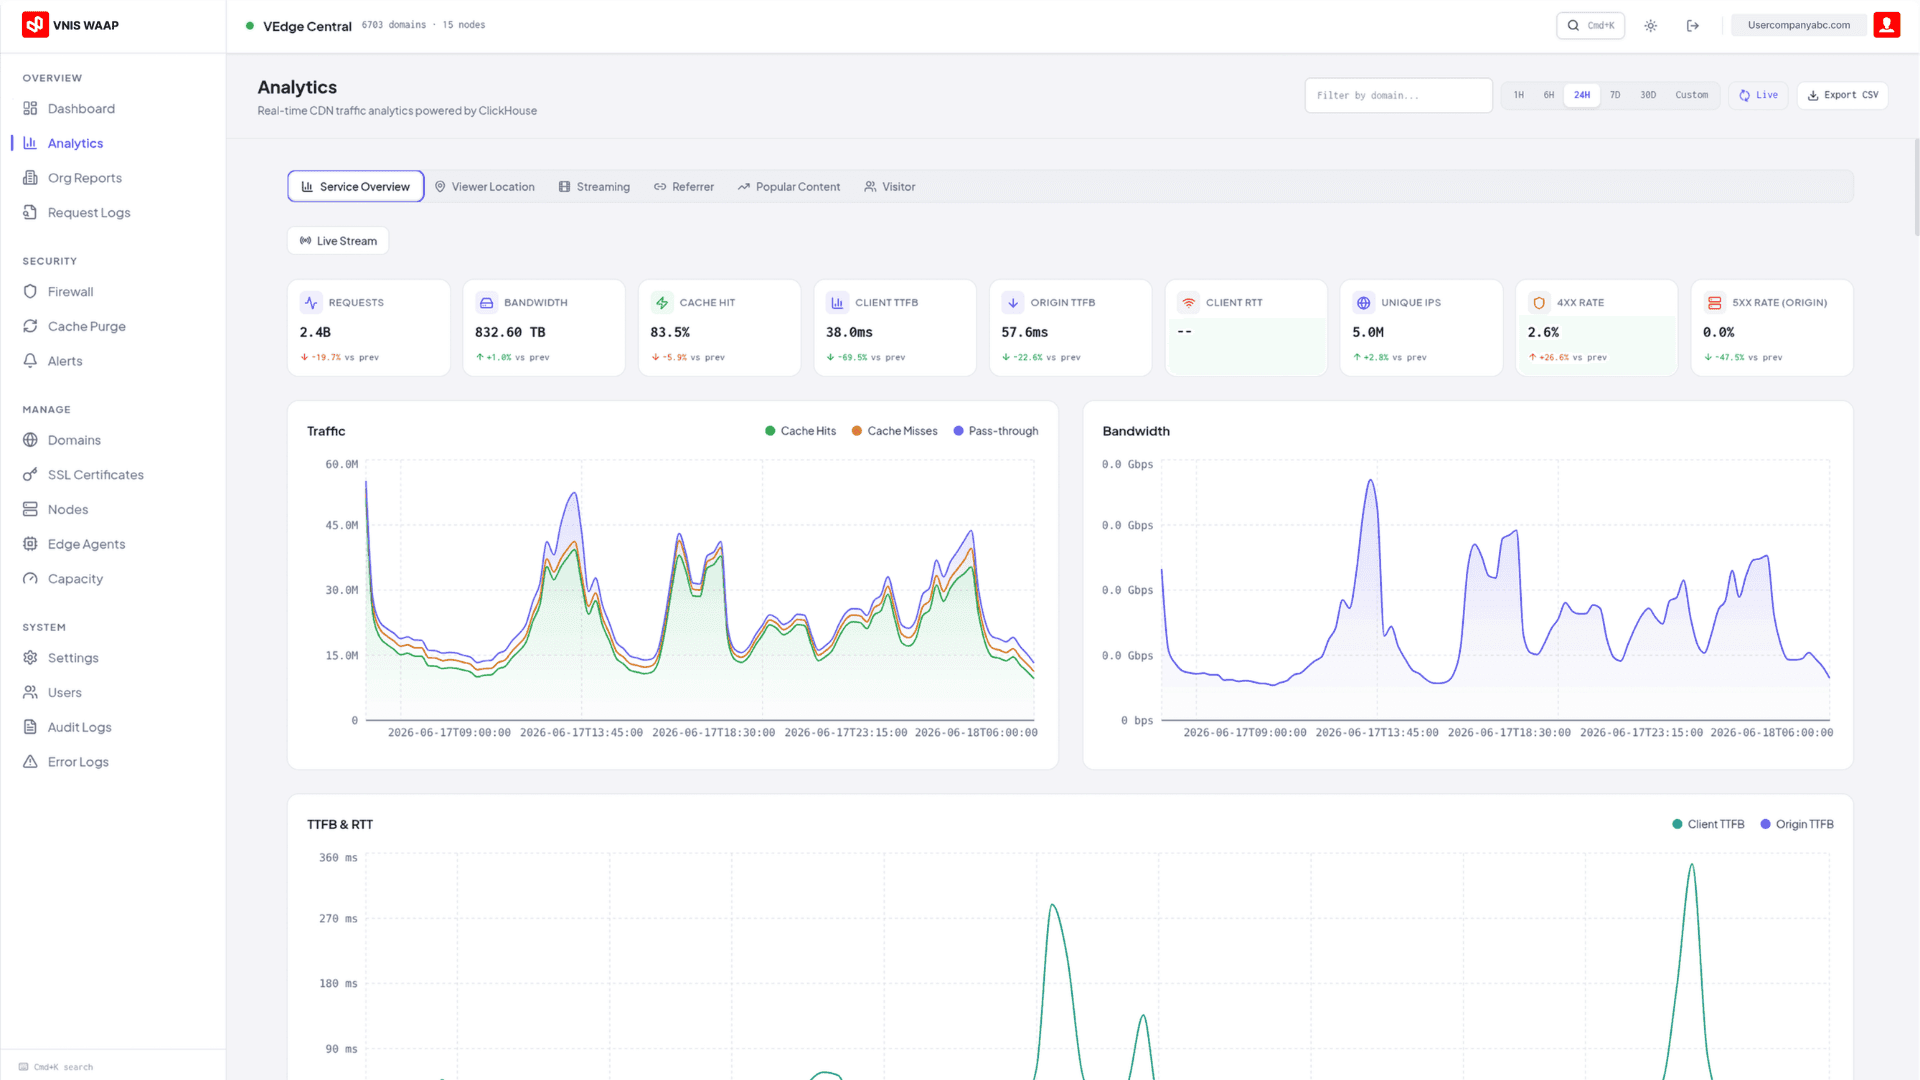
- Real-time visibility: Provides a dashboard for monitoring traffic in real time
- Compliance support: Meets the requirement to deploy a WAF under Clause 2, Article 8 of Decree 85/2016/ND-CP
Businesses can start protecting their website and applications today at no cost, with just 3 simple activation steps for WAF Free.
6. Conclusion
Protecting business data is a process that combines legal compliance, internal governance measures, and web application security technology. Businesses do not need to deploy everything at once; instead, they should start with low cost, high impact measures such as access control and regular backups, then add a web application protection layer as the system scales. Try WAF Free today to begin protecting your business data in a simple, cost-free way.
FAQ - Frequently asked questions about data protection measures
1. Which data protection measure matters most for small businesses?
There is no single measure that fits every business, but access control and regular data backup are typically prioritized first because of their low cost and clearly effective risk reduction. In addition, businesses with a website or application serving customers should also consider adding a protection layer at the web application level.
2. Does data encryption slow down the system?
Modern data encryption is optimized to minimize the impact on system performance. With today’s hardware infrastructure and encryption algorithms, the resulting latency is typically negligible compared to the data protection benefits this measure provides.
3. Are businesses required to comply with the Personal Data Protection Law?
The Personal Data Protection Law No. 91/2025/QH15, effective from January 1, 2026, applies to every organization and individual that collects and processes personal data in Vietnam, regardless of business size. Therefore, any business that collects customer data in any form needs to review its compliance status under this law and its implementing Decree 356/2025/ND-CP.
4. How does the 2025 Cybersecurity Law differ from the 2018 Cybersecurity Law?
The 2025 Cybersecurity Law (No. 116/2025/QH15), effective from July 1, 2026, merges the 2018 Cybersecurity Law and the 2015 Law on Network Information Security into a single unified document, while also clarifying business responsibilities in data protection and cybersecurity incident response. Businesses currently following the two former laws need to update to this new legal framework.
5. How does a WAF differ from a traditional firewall in protecting data?
A traditional firewall primarily controls traffic at the network layer, while a web application firewall focuses on analyzing and filtering requests at the application layer, where vulnerabilities such as SQL injection or XSS are commonly exploited to steal data. These two protection layers are typically deployed together to increase overall defense effectiveness.
6. How often should data be backed up?
Backup frequency depends on how often data changes and how important it is. For transaction data or customer data that updates continuously, businesses should back up daily, while data that changes less frequently can be backed up weekly, as long as the practice of storing multiple copies in different locations is still followed.